Sunday, November 21, 2021

Men Pretending to Be Women in Crypto

InfoSec Seinfeld do you know who else is a man?

By Dominic Alvieri

11/20/2021


She has man hands and Twitter thumbs.

Fake account and shady investment warnings. These female accounts have man hands and Twitter thumbs.


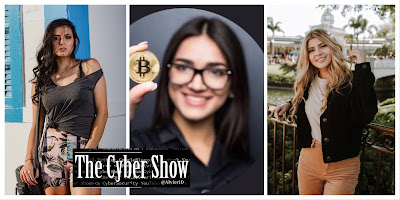
A picture tells a thousand words. A jpeg tells thousands of bytes. More actually and precious metadata. Location, camera lens, etc. These images above are the snapshots used by several woman of crypto currently online believed to operated by men.  Students, models, actors and all walks of life are used.


Stella Catrin @stellacatrin
Joined November 2021
10,000 followers. 

Today is November 21st, 2021.


This new image used above was taken by Omar Lopez and is fresh from Orlando, Florida in April and uploaded in May 2021. She is new, dangerous and readily available online for free. I would expect to see her image again. More examples to watch out for. Data points an alleged foreign man behind this Californian woman. Suspect name is unconfirmed as of posting.


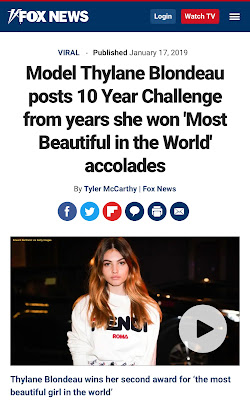
Super Model Thylane Blondeau is now crypto investor Henley Nava. Thylane has been named the most beautiful in the world. Now pitching Chinese mining among other suspect investments. 

Monday, November 22nd, 2021 addition.


Henley Nava @henleynava
June 2021
58,000 followers


Thylane Blondeau is pitching crypto?

This account has been "giving" away crypto and pitching suspect mining and crypto. The modus operandi is similar in pattern and recognition to the suspected accounts in this article. 

Another suspected fake has even more data pointing to India including Twitter handles, IP addresses, Telegram chats and more. There is even a name for the man behind one of "The Janet Trio."


The Janet Trio.


Newest active part of the Janet Trio...


Taya Janet @tayajanet
Joined August 2021
62,000 followers


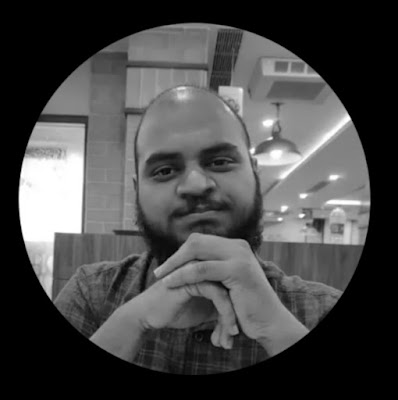
The man in the photograph is Gopal Krishna and alleged new Taya Janet. An aspiring Linux developer and failed movie critic from Mumbai, India. Irrefutable technical evidence links this man to this account. If it isn't him, he sure knows who it is. Money is on the sloppy developer.


Gopal Krishna
Joined unknown
Mumbai, India
Twitter profile...


Missed forensic link.


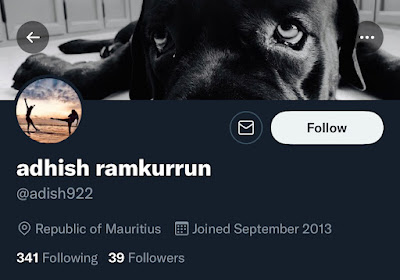
One of several missed forensic links left behind by Mr. Krishna...a link to a Twitter account.
Adhish Ramkurrun. Another forgotten fake account. Technically sloppy.

From Montreal to Minsk...and Medium.


These crypto queens above and below are retweeting the same garbage as their group. One is a self proclaimed Crypto Professor with nearly 100,000 followers on Twitter and he and the crypto queen below have very similar tweets and likes. Yesterday a Chinese mining "legit investment.' Today multiple tweets with mining and investments many registered the same day of September 2nd.

Tron[.]AC,  TRX[.]Blue and TRX[.]ST are all registered on September 2nd, 2021. All three share the same IP and have obfuscated their origins. Two of the three are utilizing a Singapore data center to forward packets to China. There are many others registered, Tron-Life, TRX[.]in...

A Russian man is operating out of Belize is behind an account. A Chinese national is also guilty of running crypto scams. Both pending confirmation.


The Professor is Gilligan


Crypto Queen @coin_mining1
Joined June 2021
40,000 followers

Associating with Russian tweets and Chinese mining.


Does anyone verify these giveaways? 


Does anyone verify these fake crypto giveaways?

The amount of crap tweeted today is unbelievable. All have tweeted again today, November 21st, 2021 The Professor is acting like Gilligan tweeting hidden Chinese based mining and other shady crypto investments.

Building a crypto followers database is as valuable a commodity as a crypto brokerage firm breach. You can cross reference data, send malicious cryptominers, clipboard stealers...

There is a new trading firm just found with ties to other crypto scams, follow up details and reveals pending.

Stay safe.


Dominic Alvieri
The Cyber Show

Tuesday, November 16, 2021

Chinese Babysitting and Surveillance Co. Ltd.

Chinese compromise domains ranging from housekeeping and babysitting services to industrial machinery

By Dominic Alvieri

Twitter  @AlvieriD


November 16th, 2021


Nearly every day new domains are acquired with company names like Nehe Maternity Matron's Housekeeping, Wengniu Teqi Housekeeping Services, Co., Ltd. and many others.
 
All are using the same IP Record No of 18dfds740-2. Every domain has a fake company name.


Over 200 domains within a 12 month period all with new fake housekeeping names and all traffic and data heading back to Beijing 


Researching this from many different machines and networks surprisingly only a VPN IP from Northern Virginia was blocked on any sites.


The domains are being acquired through multiple registrars and hosted all over the world. 
Twitter is a group favorite. Twitter has been banned in China since 2009.

Premium short domain names also include variants of Facebook, Amazon, Netflix and others...

TheStock-Exchange[.]com                     TwitterPictures[.]com              
TwitterPhoto[.]com                                 NikeAirMaxRetail[.]com                                                      Wrestlemania2016[.]com                       UrbanExchangeAZ[.]com                      
TwitterCar[.]com                                    CongressOnTwitter[.]com
HotmailSetUp[.]com                              CapiatalOneBank[.]com


Nice link.


Over 200 domains within a 12 month period. They are even using Congress on Twitter dotcom. Many of the hosts and registrars are famous for hosting and deploying malware. The links, files and traffic patterns are discernable. Malspam quickly came to a new research email once registered with one of the shams and traced back to China.


Chinese babysitting and surveillance.

TheStock-Exchange[.]com

The cover for this article is TheStock-Exchange[.]com site which has changed this week from the babysitting/housekeeping platform to a Chinese recruiting agency with several names as well. After several months of searching and countless misdirections the immutable data packets and domain traffic point to Beijing. An office building to be specific. After several contact attempts neither Luminaire, Lightning, any babysitters or communist party agents were available but probably listening. I got hung up on several times. Mention re-education and the call is abruptly over.

The customer service hotline was ice cold. So was everyone else.

Now recruiting in all areas and provinces of China including Xinjiang. 


The extensive network and multiple addresses reek of the panda with traces to Beijing.  All phone numbers are in Beijing with a call center in Germany another favorite asset. Other fake companies are being utilized in different industries and are following the same modus operandi including an industrial packing company which is active in attempting to sell to United States based companies.

I have not been able to locate any of the non-existent packaging equipment export companies but they do respond. All the files, links and traffic patterns are the same. They will respond for a quote but beware of malspam that will follow.


My favorite name so far is Guangzong Multifunctional Pillow Packaging Machine Factory. It is easy to find the air quality in Guangzong, China. Finding information about the packing company is another story. Shenzhen has no listing either.

Guangzong Multifunctional Pillow Packaging Machine Factory is linked to Beijing


Air quality in Guangzong is easy to find.


Hug the Big Panda


None of the industrial packing company names are real or have any listings in any of the major Chinese exporters websites or shipping port transfer agents. One way or another the data points to this one block in Beijing, 

Visitors beware there is a bit of a pattern developing.


Stay safe online and off.


Dominic Alvieri    @AlvieriD

The Cyber Show

Monday, October 18, 2021

Hovering Over a Link is Not as Safe as You Think

Decoding HTML is not illegal but this line of code should be


By Dominic Alvieri

October 18th, 2021


Cybersecurity Awareness Month


Twitter was abuzz this week when inspecting HTML elements came to the headlines with the Governor of Missouri threatening to prosecute a reporter for simply viewing readily accessible web site code and attempting to help rectify the problem. The Governor is unaware of the basic structure of a website. Everyone can F12.

What is HTML? HyperText Markup Language (HTML) and Extensible HyperText Markup Language (XHTML) are the foundational coding languages and technologies of designing web pages. 

But do you know HTML? What is XHTML?  Is it CSS or XSS? You need one for style.
Luckily I happen to know both.

Dropper files, phishing kits, payloads...

We are at HTML5 and HTML file paths are used to find the geolocation of a user. 


Info security.


The latest from Info Security by Dan Raywood is the Top Ten Ways to Detect Phishing above. 

Hovering over a link was not on the list.


Cybersecurity Awareness Month


There are several ways to weaponize a link and a hover and script to a link. A hover over instance of malware is not new. Zusy banking trojan comes to mind but it was easily detectable because you needed to open a Microsoft PowerPoint first. You did not need to enable macros or JavaScript for the dropper file to download the malicious trojan. 

No click was needed either, just hovering over the link. 


So what does this all mean today?

There are several different variants and tricks that can be coded and multiple languages and programs to fool the unsuspecting visitor after arrival to a web site and page. Basic HTML coding will be required for all web pages as a basic framework. Finding the location beforehand is essential for all. Cyber security practitioners should be aware of the changing threat landscape. Phishing accounts for the vast majority of initial network entry for malware, 89%, and malware deployment, 95%,  according to Sans, Info Security and others. 


Start with the basic terminology


Markup Language


By definition a set of symbols or tags that allow you to render text on a web browser or in print.


SGML


Standard Generalized Markup Language defines the syntax of a markup language.

HTML


HyperText Markup Language files enable navigation from one page to another web page via links invented by Tim Berners-Lee in 1989. HTML is defined syntactically by SGML. The main difference between HTML and XHTML is basically syntax-based rules. HTML was created basically for text while XHTML is more dynamic and defined.

XHTML


Extensible HyperText Markup Language is a combination of XML and HTML and has been a World Wide Web Consortium (W3C) recommendation since 2000. XHTML is based on XML which is restrictive and stricter than more lenient HTML. It is used for more consistent display across browsers to accommodate for mobile browsers.

XML


Extensible Markup Language is a subset of SGML and used to define the syntax of a markup language. You can create and define elements. Elements are a set of instructions.

CSS


Cascading Style Sheets are a set of rules to define the appearance of a web pages color, style, etc. There are three types of Cascading Style sheets: embedded, inclined and linked.

Elements


Elements are a set of instructions.

TAGS


TAGS are indicators and are used to identify the type of content in this section. There are many types of TAGS such as <h1>,  <span> etc. Opening and closing TAGS are required. <title></title>.  For empty elements the slash would follow the tag to be syntactically correct,  <tag/>.


Attribute


An attribute is a part of an element that modifies the characteristics of that element.

JavaScript, PhP, Python...more to know.


An email, a mobile site or a traditional web page can all be manipulated differently. These are the simple basic terms of one of the many ways used to manipulate a malicious link.


Mouse over script in an HTML element 


Apple mouse over script example.

October 13th, 2021 CNBC article about the new iPhone Watch series 7 has a blue underlined hyperlink with the text "Apple" in the first sentence of the paragraph, also know as an HTML element. Where does it take you? Implicit trust is implied with a reputable site such as CNBC so trust shouldn't be a major concern in most cases. A programmer from CNBC most likely.

The web page was coded this way.

Technically the link can lead anywhere if you do not inspect the element. Attacking the host site and other entries are topics for another day. Lets focus on the simple things first. I was expecting the link to go to the Apple website but instead it was coded and directed to CNBC's Apple stock quote below.


Apple stock price 10/13/21

What coding is required to enable or disable functions of an element? JavaScript? Python?


The Apple example above is technically an HTML element. There are several ways to accomplish obfuscation of origin but with simple HTML you can code as you wish. You can change styles, fonts, links, text and input the address you want to show on the mouseover, or your hovering script. You can even disable the hover over script. How about blocking the security feature in an email that shows the address when hovering? Sound easy? Let us drill down deeper.


Disable hover text over an HTML element


visibility: hidden;


Here is a tool tip. I just disabled the hover over text on this HTML element by hiding the visibility. By removing the hover text script now when you hover over the text there is no hover over the text showing again hiding the actual link or any text. 

Creating believable, clickable copy text is the next step in making you click. 


The line to locate is <a href


It isn't the line, it's how you use it. 


Much like real world real estate, virtual real estate is all about location, location, location. There is another way to code the location but lets stick with the basic that is known rather than educate the nefariously minded phisherman should one come across this.

href basics indicate actual location in quotes > followed by text to show.


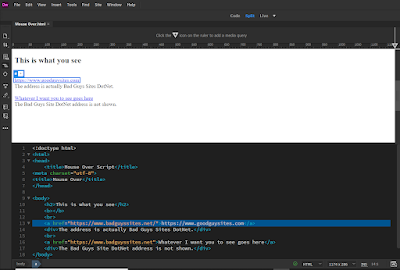
<a href="Actual address of this link">What I am showing you goes here</a>


Link address is dictated by the location attribute in the href element shown highlighted in line 13 of code below. Line number will vary depending on site and complexity. Very easy to code and see.

It is as simple to code as entering text and seeing it is as easy as inspecting an element. Be aware of redirects, MiTM, MiTMO and other tactics, but the basic address of where you are going is shown.

The actual location goes first and is in quotations, ""> with text component to follow before closing the tag, </a> in <a href example above. It is all in the code.


HTML code of sample site.


For the early stages I have not coded any CSS or JavaScript yet so we are just creating the basic frame. This one line of HTML code determines the location in the href element and additional text can obfuscate or add to the ploy. 

Be aware of actual location and ip address, among other things.


Hover over text in an email


Playing with location in an email


The following email was obfuscated without any header spoofing which is another topic. 

Adding to the deception most email platforms will let you input your desired location and text. Below you can see the safelinks protection status in Outlook. I created the text to look like a secure, safe link.


Email spoofed and changed.


The hover over email


Other security features for the email hover over include showing the destination address at the lower left of the screen. Working on a bounty to disable an email hover over but it requires more work and I have had inconsistent results so far. Full details will be released at a later date after completion and repair or patch.

The security location bar at the bottom left of the screen does not disable so far, but what if you created your own camouflage pop up to block or surround the actual location message may be an option and an alert.

How easy is it to get safelinks protection status?


The idea is to protect the user and not give away too many secrets to cyber criminals but it is no big secret that garnering safelinks status is quite easy. The header and other coding will be adjusted and not discussed here. This isn't a how-to-hack guide. 

Insert link as you wish.


Hover over text in a smartphone?


Yes. On Apple iPhone and most modern smartphones just lightly tap and hold and security pop up appears. Please note the safelinks status. This is actually safe and from NIST, the National Institute of Standards and Technology.


NIST cybersecurity week.


This Facebook link below actually leads to my Twitter profile. 


I deleted my Facebook account last year


As always be aware of where you click or even hover.

 Always look for the actual location and do not take blue text for what it is worth. 

Stay safe. More blue text.


Dominic Alvieri
 

Saturday, October 2, 2021

The Binance 500

Binance Online Investment Fraud Accelerates


October 2nd, 2021

By Dominic Alvieri


The Binance 500


Binance is not sponsoring a new NASCAR series


Over 500 new Binance themed phishing, investment scam and fake exchange domains have been registered this past week. Exactly 2,500 have the word "Binance" name included in the titles. Usual variants containing hyphens and incorrectly spelled domains account for an additional 141 bringing the weekly Binance domain fraud count to 2,641 new malicious domain possibilities.

Several of the new domains are now active


                                               Binance-Investments[.]ltd


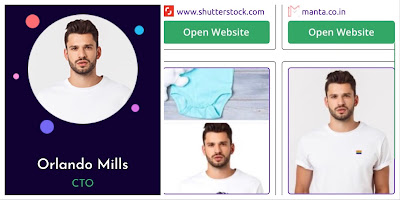
Meet Binance Investments Chief Technical Officer Orlando Mills


Underwear model and readily available image online.


CTO is underwear model and Shutterstock image.
CTO is an underwear model and on Shutterstock.

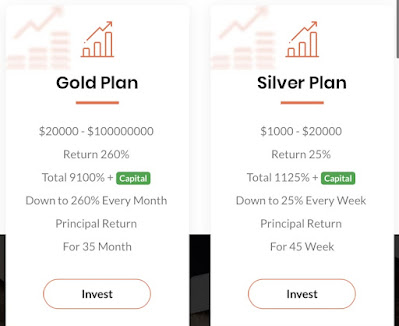
The investment scam on Binance Investment dot ltd is the classic scammer amazing return story. This office is from Singapore and site was originally hosted in Finland. mid=blog this site appeared to host from the Unoted States and finally suspended after several reports sent. Binance-Financial[.]info and a host of others shown below. The firm names may change but the scam is the same. Send us some crypto and we will send you back more...and fast.


Several more "plans" are available to choose from.


Binance investment scams.


The cache of new domains include phishing, investment fraud cryptomining malware. The majority of this past weeks domains are the infamous .xyz ending lovelies. New Binance phishing sites activated this week include a "Binance form" link which is being emailed shown below. 


                                                    Binance-Form[.]com

New Binance phishing site.


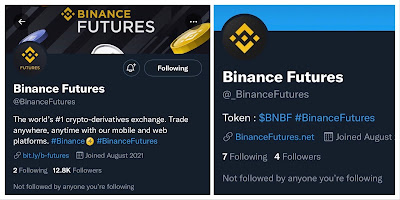
Other frauds include former fake exchanges XBinance and a fake Binance futures variant. Any one of the sites can be set up to deploy malware quickly now with RaaS available to even the most inexperienced script kiddie. Secure 404 with a dead link.


Real versus fake Binance profiles.
The real account is on your left.


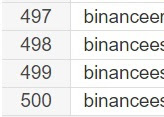
500 domains with the word Binance were registered this week.


500 Binance domains registered this week.
500 new Binance domains. Courtesy of DnPedia.


Legally registered disclosures usually mean they are not. This is a US based site attempting to pull of the incredible returns of 10-25% per day. Early retirement does sound great.

First series of Binance scams reported on the Twitter link below, @AlvieriD


Twitter @AlvieriD


One site even have the word scam in it. BinanceScam[.]exchange with a secure 404 page and odd deployment message. Ahh, it has to be ok. Right?


The Cyber Show by Dominic Alvieri
Not on Facebook

Twitter @AlvieriD

The Kremlin, Politics and Ransomware

Qilin Ransomware caught with politically motivated fake document (and old data) in post. by Dominic Alvieri March 8th, 2025 @AlvieriD Was it...