Showing posts with label Coinbase. Show all posts

Friday, February 3, 2023

I Can Name That Exploit in One Note

 Another New Day and Another New Way...


By Dominic Alvieri
February 3rd, 2023

The Cyber Show, by Dominic Alvieri.


Do your steganographic skills suck? Never fear 2023 is here. I guess I wasted years practicing the dark art of stego now with so many new ways to discretely infect, compromise and take over your target. 

How? Hiding your malicious file in an empty element is one way recently disclosed by researchers. Needless to say there are several other ways to play around with elements.


Another popular choice... embedding a malicious file within One Note. 


One Note.

You can't hard code all of your website. It's just not practical. Now that Microsoft has disabled macros threat actors are finding new ways to infiltrate networks. One Note has taken center stage and Microsoft Visual Studio just joined the fray. 

Here is a short list of files to closely examine or block that are being abused by TAs

.msha
.htm
.lnk
.js

You can do this with many different files and ways.

Ill leave you with this partial...

c:\ encrypt files
\"what?"\ attrib -h (?) -r  ("nice-try")

Redacted


Tuesday, February 22, 2022

Banking and Crypto Stealing 2FA Bots on Telegram

Telegram Channels are Behind Evil New Ways to Separate You From Your Money


By Dominic Alvieri


2-22-2022


Telegram has had a history of security breaches, bad actors and security issues for several years. More and more malicious actors are using the platform along with 300 million others. Recent examples during the Russian invasion of Ukraine are showing an accelerating trend of cyber activities on the platform including the SberBank breach disclosed below.


SberBank breach files.

Other recent troubling requests


The Telegram mobile protocol MTProto protocol is proprietary and has had security questions for years. Cryptographic issues aside the desktop version does not use the protocol and storers all data in plain text. Plain text is also an issue with the mobile virtual cloud set up. 

In simplistic terms all data is stored on Telegram servers and not end to end encrypted (e2ee) by default. There is a secret chat option that does but that is another story. No e2ee by default leaves millions at risk from an advanced attacker. 

The current state of the gram


Underground forums and marketplaces are nothing new for a bad actor looking to score some low grade malware, stolen credit cards or a phishing kit. No need to fire up the TOR browser now because these items are becoming more mainstream available on the web and malicious Telegram channels.

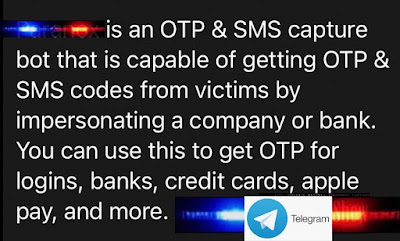
OTP 2FA password stealing bots are being packaged with hand selected robocall features like foreign language accents to target customers of specific countries. Two if these bot services have been verified as working account stealing bots and recent reports of usage and abuse has been reported.

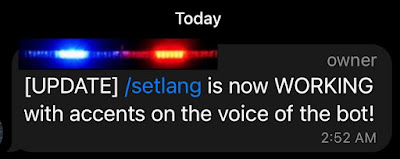
New set language feature   /setlang   


Set language /setlang


Bank of America, Chase and Wells Fargo are among the banks that these bots works with stealing your one time password or 2FA login. Several cryptocurrency platforms are also being marketed with automated bots and classes.


Several channels are selling various One Time Password (OTP) and 2FA stealing bots. Having verified two of the products here is a breakdown of some of the malicious capabilities.

Packages are readily available for Apple Pay, banks, crypto....


OTP 2FA Password stealing bots


Vendor P above has been active in advancing the bots attack capabilities in the past week adding Bank of America and Chase to their hackable list. Security support teams at Bank of America, Chase and Telegram have been notified. 


Here is what the bot can do. The ability to go after anyone with just the minimum information that would be needed to carry out this attack is worrisome. Basic OSINT research. 

As simple and annoying as this scam is the technology behind the maliciousness does work.

Enter target data, select a few options and assets to acquire and the nightmare scenario begins. Like most malicious activities they do require at least one action from the target, barring a zero-day, zero click exploit.

Video snapshot of working bot in action


Robocalls blanket the target with messages of an account breach and that verification is needed. An extreme sense of urgency is created and conveyed in the robocall accent of your choice. The artificially curated voices of the bot repeatedly mention your account is at risk and require you to verify your account via an OTP or your 2FA verification.

Partially redacted for security.

Everything is the same as before...


We have come along way from just unlocking iPhones.


What else can this bot do?


New functions which have just been posted and untested include bypassing:
-Authy
-Google Authenticator
-Microsoft Authenticator

Several variations of the original bot are online and to no surprise many claims are stretched and many are just outright frauds.


Relentless requests are the first step and if entered, the near-instant theft takes place. When a verification code is entered the bot executes the code, enters the account and transfers all of the cash or cryptocurrencies out of the account within minutes. In this live research example a crypto account was used and emptied within 2 minutes of the final string of data obtained by the bot. Crypto firm name withheld. 

Several other options are available if the first level attempt via robocalls fail to capture the required codes. These are actual working multifaceted bots able to spear or whale nearly anyone.

What can you do? DO NOT INTERACT

Do not interact with any SMS, email, link or call regarding your breached accounts. Always go directly to your real account through and official site or representative.

Go directly to any account in question and the official site and or contacts and avoid any "urgent need" to give your information to anyone. Chances are you haven't been hacked but someone sure is trying.


The Cyber Show
by Dominic Alvieri

Twitter @AlvieriD

Monday, February 7, 2022

Crypto Professor Failing Ethics 101

Self proclaimed crypto professor promoting dubious crypto projects and outright frauds.


By Dominic Alvieri


2/06/22


The Cyber Show by Dominic Alvieri


Self proclaimed crypto professor, enthusiast and promoter of all things crypto Serkan Arikan has amassed a small army following pushing giveaways in Bitcoin and Ethereum and coming up with great 100% legit investments.

Whenever anyone mentions their investment is 100% legit it probably isn't. This professor likes to pitch whatever the coin or project du jour is as long as it pays him 30% or more of your investment. Giving away $8,000 to non-existent lucky winners in Ethereum almost every day. These promoters really aren't giving away $50k a week. The lure of easy money still has a very strong appeal. There are no verified winners. Only Twitter and the actual accounts know that. 

Watch out for rug burns.

Here is a clue of some of the chicanery...


Speaking of chicanery, how many accounts do you have professor?


No actual links to websites attached.

Snapshot of profile picture for account mentioned in article @SerkanArikan06 


There appears to be more than two accounts which wouldn't shock anyone. Blog updates will follow pending confirmation.


Actual professor found in turkey in red.


Outright Fraud


Here is what we know. The Twitter account for the crypto promoting Serkan has swelled to over 140,000 followers with fake giveaways, dubious offshore mining ventures and outright ponzi-type frauds. Payouts to Arikan average 30% and go as high as 80%. 

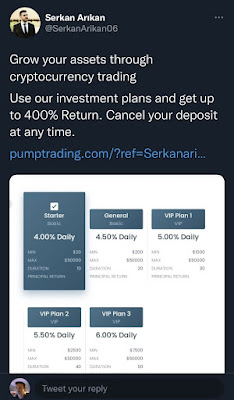
Below are several professor backed ventures that have been closed and tweets about the said projects that have been deleted. Most recently Pump Trading offering illegal and impossible daily 6% returns.

Deleted tweet for closed ponzi-type crypto fraud Pump Trading. This is the third attempt using the same template, registrar and scam.


Deleted tweet for closed fraud.


Pump Trading  pumptrading.com (Closed)


Cryptolle (Closed)


Cryptochain Tech (Closed)


The same crypto template has been used by this account peddling fraud. Some of the other 100% "legit' investments include Chinese mining ventures after China barred crypto mining. Other dubious mining facilities were located in Panama and Vietnam.

The common mining theme? Every project has referral fees going to the professor in the 30-80% range. That is 30 to 80% of your investment. What type of investments can afford those type of payouts?

None. Rhetorical question.


The professor has pitched tron[.]ac from Singapore which shares the ip address with the above tron[.] blue. How many of these Tron mining ventures are they. How many are real? Don't forget about tron[.]st and all the other high referral fee projects being pitched. Literally moments ago this account tweeted a promotion for tron[.]pe registered with Gandi and appearing to originate in China. 

China banned crypto mining yet again the professor is pitching what appears top be another new mining venture originating in the banned communist state. 

Watch out for rug burns.


More than just dubious mining projects. Be on the lookout for any suspicious offers. Someone is usually getting paid something and promoters have been known to flee. That is the definition of a crypto rug burn.

Nothing is for free. If it is free you, your data or your crypto are usually the commodity. 

Just because it is online doesn't mean it is real. There is no UFC token,


This is not a real token.,
This is not a real UFC token or link. 


It is a fight and the struggle is real. Stay safe online and off.

The Cyber Show
by Dominic Alvieri @AlvieriD

Monday, January 10, 2022

Top New Crypto Scams of 2022

Fake Offerings, Giveaways and Frauds Continue


By Dominic Alvieri


1/11/2022


Crypto scammers are out again pulling some of the same scams we have seen in the past few years. Ransomware groups continue holding corporate and personal data hostage. Bitcoin has retreated in price and the mainstream crypto space has also cooled but the crypto scam market is white hot.

In the first week ending January 7th, 2022 there were 3,716 new domains registered with the keyword "token" and the vast majority being developed are scam related projects.

Giveaways and fake AirDrops continue.


Here are some of the highest risk fake projects to look out for in 2022


Meta Token (Closed)

Facebook rebranding to Meta changed the crypto scam landscape late last year. Several fake Meta coins and tokens have appeared and are registered. Meta token, coin below is now closed (1-8-22) registered as Meta token presale below.


Fake Meta token presale site.

Fake Meta token site taken down.


This fake Meta token even had the Meta CTO Andrew Bosworth listed as Corning CEO on their site. They are not very good at this.

Meta CTO moonlighting on this crypto scam?

Several more Meta related token and coin scam sites have been registered and attempted with more to come this year. Watch out for Meta related scams.

MetaMask Token (Live)


New MetaMask token site has popped up with this fake offering.

metamask-token[.]net


Fake MetaMask token site.

Fake AirDrop for a fake token


Fake MetaMask token AirDrop.


No security vendors have tagged this as of 1-10-2022.


Baby MetaMask (Reg)


Several Baby MetaMask versions including babymetamask[.]com are in the works. There is no official MetaMask token or coin.

Twitter Token (Live)


New Twitter token attempt is still ongoing at twittertoken[.]live after reporting it to Twitter and authorities in late 2021. The site and telegram channel are still up.


Unofficial Twitter token is still live.


Fake Twitter token Telegram channel.


Be on the look out for other fake offerings from any major corporation. Complicating matters in the announcement that PayPal may be offering a token of their own. Stay tuned for details in the next few weeks.

Other new notables:


Instagram-giveaway[.]com

Amazon, Etsy, GM...

BabyMetaCoin[.]net/xyz...


Elon Musk, Jeff Bezos and other famous names are being used.


We have all seen the Elon Musk related cryptocurrency scams but several other top names are also being utilized...misrepresented as endorsing a fake token or coin.


Seed phrase phishing is on the rise

Watch out for continued seed phrase and password phishing on crypto related accounts and assets.


Seed phrase phishing.


Use MFA. Cold store your crypto. Be aware of any offerings or yields that are well above market and please do your due diligence.

Stay safe.


The Cyber Show
By Dominic Alvieri
@AlvieriD

Thursday, December 30, 2021

Crypto Scam Year in Review 2021

 Crypto Scams From ADA to Z


By Dominic Alvieri

12-31-2021


Cryptocurrency price records were challenged by volume records of crypto scams this year. Broad Wall Street adoption brought out fraudsters from all corners of the world. Coinbase and Robinhood went public this year and zero-day exploits broke records. Elon Musk became the ultimate crypto spokesman.


Wall Street adopts crypto.


Crypto exchanges, DeFi platforms and personal accounts were hacked. Verified social media accounts were breached to further expand crypto fraud this year. Several instances of leveraging smart contract exploitation begins with (redacted)

This is a hacked Twitter account below that attempted a Binance giveaway scam. 


Hacked account pitching a Binance scam.


January roared in this year with the events at the Capitol Building on January 6th, 2021. Financial and criminal litigators sharpened their pencils and went to work. Besides the slew of criminal prosecutions cryptocurrency regulation framework was hashed. Crypto regulation is coming sooner rather than later. 


Stable coins are under reporting assets and deficits abound. Stable coins require serious attention from regulators in my professional view.


SEC requesting crypto information.


Elon Musk became the spokesman for cryptocurrencies this year even making an appearance on Saturday Night live sparking a selling frenzy. Crypto traders hang on to every tweet and make split second decisions in the middle of the night based on Elon's words.

Scammers took note.

Elon Musk themed crypto scam.


Elon Musk themed crypto scam.


One of the many Musk memes


Endless cryptocurrency frauds

Hurry up and take part in all of the fake giveaways using any name and company to gain your trust and get your digital assets.

MicroStrategy


MicroStrategy themed crypto scam.


Cardano

Giveaways, Events and AirDrops are all ways to say good bye to your crypto.


Charles Hoskins themed crypto scam.


Twitter


Social platforms and anything that could make a buck was used. Twittertoken.[live] is still active. Several variations were attempted this year. BEP20 tokens made it easy for anyone to issue just about anything.


Winklevoss twins


Winklevoss twins themed crypto scam.


Boss Baby themed crypto scam


Boss Baby themed crypto scam.


Baby Coin Mania


Young Elon.


UFC-Fantoken. Not a fair fight just fraud.


UFC themed crypto scam.


Account credential phishing skyrocketed


Gemini phishing.


Ponzi-type crypto scams came back


These scams are not new but have come back with a vendetta this year. Send me one coin or token and I'll send you one back is a scam that has been around since Bitcoin began. Social media accounts have been big promoters of this old hoodwink.

Promoters or just outright crypto scammers?


Spider-Man token again timed with new movie launch


Spider-Man token again?

Bonus


Crypto miner coming with bootleg torrent download of new Spider-Man movie. 

MetaMask fake support(s)


8 fake MetaMask support accounts.


Year end holiday scam rush


Over 600 crypto scams have been personally reported and I can't list all the crypto scams this year but this gives you an idea into the year of zero-days and crypto scams this 2021 has been. Log4J critical logging exploit exploded on the scene late this year and will no doubt have a lingering impact.

Happy New Year

Crypto scams continue even on New Year's Eve and I'm sure I'll catch at least one on New Year's Day.

Crypto scams are not going away anytime soon.


New Year's Eve crypto scams.


How do the scammers get away with it?

In many cases they just don't give anything away at all. One new Twitter account allegedly gave away over $81,000 in under one month. Other instances have the scammers just recycle the crypto giving a token amount to a controlled account.

No one is auditing these giveaways. 


A so called "Crypto Professor" with 120,000+ followers even set up a trading firm and site which have been closed. The site alleged an unsustainable 4-6% daily return, ie scam. Coming in January.


Meta New Year

Not from Facebook or Meta.


Meta New Year?


Do your due diligence 

If it sounds like a duck...


The Cyber Show by Dominic Alvieri.

The Cyber Show
by Dominic Alvieri
Twitter @AlvieriD

The Kremlin, Politics and Ransomware

Qilin Ransomware caught with politically motivated fake document (and old data) in post. by Dominic Alvieri March 8th, 2025 @AlvieriD Was it...